Code-hosting integrations
Weblate integrates with code-hosting sites in several separate places: repository access, incoming notifications, and pushing translations back. The exact setup depends on whether you use Hosted Weblate or run your own Weblate instance, and on whether Weblate should push directly or create pull or merge requests.
Utilisez cette page comme une liste de contrôle destinée aux développeurs. Les pages de configuration individuelles restent la référence officielle en matière de syntaxe de configuration.
Setup overview
Donnez à Weblate l’accès au dépôt.
Pour les dépôts GitHub sur Weblate hébergé, utilisez l’application Weblate hébergé via le parcours Connecter un compte GitHub de Weblate. L’application donne à Weblate hébergé un accès aux dépôts sans inviter l’utilisateur hébergé weblate.
Pour les autres dépôts de Weblate hébergé, et pour les poussées SSH directes en dehors du parcours de l’application GitHub, ajoutez l’utilisateur hébergé weblate là où il est disponible, voir Accès aux dépôts à partir de Hosted Weblate.
For self-hosted Weblate, create a dedicated code-hosting user and grant access using Weblate’s SSH key or an HTTPS token, see Accessing repositories on code-hosting sites (GitHub, GitLab, Bitbucket, Azure DevOps, …).
Configurez Dépôt du code source afin que Weblate puisse cloner le dépôt.
Configure incoming notifications so Weblate pulls changes soon after a push. The repository webhook or app must point to the matching Weblate hook URL, and the project must have Activer les points d’ancrage enabled. Component Dépôt du code source must match a repository URL from the webhook payload; see Matching webhook targets.
Choisissez la manière dont Weblate doit renvoyer les traductions :
Utilisez Git ou Mercurial et URL pour l’envoi du dépôt pour effectuer un push directement.
Utilisez un backend VCS spécifique à un fournisseur, tel que GitHub ou GitLab, pour créer des demandes de pull ou de fusion. Ces backends nécessitent des identifiants API dans les paramètres de Weblate.
Vous pouvez définir Pousser la branche si vous souhaitez que Weblate effectue un push vers une branche du dépôt en amont plutôt que d’utiliser une fourche, lorsque cela est pris en charge.
Envoi des modifications depuis Weblate
Each translation component can have a push URL set up (see URL pour l’envoi du dépôt), and in that case Weblate will be able to push changes to the remote repository. Weblate can also be configured to automatically push changes on every commit; this is enabled by default, see Pousser lors du commit.
Si vous ne souhaitez pas que les modifications soient poussées automatiquement, vous pouvez pousser manuellement sous Maintenance du dépôt ou via l’API avec l’option wlc push.
Si vous ne souhaitez pas de poussées directes de la part de Weblate, il est possible d’utiliser Requêtes de fusion GitHub, Requêtes de fusion GitLab, Tirages Gitea demandés, Requêtes de fusion Pagure, Poussées Azure DevOps demandées ou les révisions Gerrit review requests. Vous pouvez les activer en choisissant GitHub, GitLab, Gitea, Gerrit, Azure DevOps ou Pagure comme Système de contrôle de version dans Configuration des composants.
Dans l’ensemble, les options suivantes sont disponibles avec Git, Mercurial, GitHub, GitLab, Gitea, Pagure, Azure DevOps, Gerrit, Bitbucket Data Center et Bitbucket Cloud :
Configuration désirée |
|||
|---|---|---|---|
Pas de push |
vide |
vide |
|
Pousser directement |
URL SSH |
vide |
|
Pousser dans une branche séparée |
URL SSH |
Nom de la branche |
|
Pas de push |
vide |
vide |
|
Pousser directement |
URL SSH |
vide |
|
Requête d’extraction GitHub à partir du fork |
vide |
vide |
|
Requête d’extraction GitHub depuis la branche |
URL SSH [1] |
Nom de la branche |
|
Demande de merge GitLab à partir du fork |
vide |
vide |
|
Demande de fusion GitLab à partir de la branche |
URL SSH [1] |
Nom de la branche |
|
Gitea merge request from fork |
vide |
vide |
|
Gitea merge request from branch |
URL SSH [1] |
Nom de la branche |
|
Demande de fusion Pagure à partir d’un fork |
vide |
vide |
|
Demande de fusion Pagure à partir de la branche |
URL SSH [1] |
Nom de la branche |
|
Azure DevOps pull request from fork |
vide |
vide |
|
Azure DevOps pull request from branch |
URL SSH [1] |
Nom de la branche |
|
Gerrit review |
URL SSH |
Target branch name (optional) |
|
Bitbucket Data Center pull request from fork |
vide |
vide |
|
Bitbucket Data Center pull request from branch |
URL SSH [1] |
Nom de la branche |
|
Bitbucket Cloud pull request from fork |
vide |
vide |
|
Bitbucket Cloud pull request from branch |
URL SSH [1] |
Nom de la branche |
GitHub
GitHub repository access
Hosted Weblate GitHub App
Sur Weblate hébergé, la configuration recommandée consiste à connecter l’application Weblate hébergé depuis l’espace de travail Weblate où se trouve votre projet. Utilisez le parcours Connecter un compte GitHub, installez l’application sur l’utilisateur ou l’organisation GitHub qui possède vos dépôts, donnez-lui accès aux dépôts que vous souhaitez traduire et importez les composants depuis le compte GitHub connecté.
Le flux de travail basé sur l’application utilise des jetons d’accès d’installation GitHub pour cloner, pousser des branches de traduction, créer des demandes de tirage et recevoir des notifications entrantes. Vous n’avez pas besoin d’inviter l’utilisateur GitHub weblate de Weblate hébergé ni de configurer un webhook de dépôt séparé pour les composants importés de cette manière.
Utilisez l’utilisateur GitHub weblate de Weblate hébergé uniquement lorsque vous configurez intentionnellement des poussées SSH directes en dehors du flux de travail de l’application GitHub, voir Accès aux dépôts à partir de Hosted Weblate.
HTTPS avec jeton d’accès personnel
For a single private repository, HTTPS access with an access token is usually the simplest setup when the provider supports Git over HTTPS. Use the provider-required username and token in Dépôt du code source.
Configure URL pour l’envoi du dépôt only when Weblate should push changes directly or when the chosen workflow requires a push URL, see Envoi des modifications depuis Weblate.
The token needs read access for cloning and write access for pushing. Provider-specific VCS backends that create pull or merge requests might require separate API credentials.
Pour utiliser cette approche :
Créez un jeton d’accès personnel comme décrit dans Création d’un jeton d’accès pour une utilisation en ligne de commande.
Incluez le jeton dans l’URL de votre dépôt :
https://username:token@github.com/owner/repo.git.
Cette approche convient lorsque vous débutez avec Weblate ou travaillez avec un seul dépôt.
SSH with a dedicated user
For setups with multiple repositories, use SSH access with a dedicated code
hosting user for Weblate. Add Weblate’s public SSH key to that user, grant the
user access to the repositories, and use SSH URLs in Dépôt du code source,
for example git@example.com:group/project.git.
Configure URL pour l’envoi du dépôt only when Weblate should push changes directly or when the chosen workflow requires a push URL, see Envoi des modifications depuis Weblate.
This also avoids provider restrictions on SSH key reuse. Some code hosting sites allow a public SSH key to be added only once, or only to a single user or deploy key entry. Keeping Weblate’s SSH key on a dedicated user lets that user be granted access to multiple repositories without reusing the key in several places.
This keeps personal, project, or API access tokens out of repository URLs. Provider API credentials are still needed when using a provider-specific VCS backend to create pull or merge requests; those credentials are configured separately from the Git repository URL.
Pour GitHub, créez un utilisateur dédié, par exemple weblate-bot, et utilisez des URL SSH GitHub pour vos dépôts, par exemple git@github.com:owner/repo.git.
On Hosted Weblate, use this SSH-user workflow only for direct SSH pushes outside the recommended Hosted Weblate app workflow.
Note
When using GitHub for pull requests, the Pousser la branche configuration affects the behavior: if not set, the project is forked and changes are pushed through a fork. If set, changes are pushed to the upstream repository and the chosen branch.
GitHub notifications
Weblate intègre une prise en charge native de GitHub.
If you are using Hosted Weblate, use the Hosted Weblate app from Weblate’s Connect GitHub account flow. It uses GitHub App webhooks, so you do not need to configure a separate Webhook in GitHub. Components imported from the connected GitHub account also use the App for repository access and pull requests, without inviting the Hosted Weblate weblate GitHub user.
The Hosted Weblate legacy app is kept for existing webhook-only setups. Its deliveries use the generic GitHub webhook URL and are authenticated using a separate webhook secret configured by the Hosted Weblate operator. Use it only when you need the legacy app to deliver GitHub notifications to Hosted Weblate.
For self-hosted Weblate, register the GitHub App using the in-app registration flow described below. Weblate generates the App manifest, GitHub returns the credentials, and they are stored in the database - there is no settings-based configuration.
Registering the GitHub App from Weblate
The fastest way to add the GitHub App is to let Weblate generate a GitHub App manifest with the correct permissions, events, and webhook URL pre-filled:
Sign in to Weblate with an account that has management access.
Open Manage → Code-hosting connections → Register Weblate GitHub App.
Fill in the form. The GitHub host defaults to
github.com; change it to your GitHub Enterprise hostname if needed. Leave Organization blank to register the App under your personal account, or enter an organization slug to register it under that org.Click Continue to GitHub and confirm on GitHub’s Create GitHub App page (you can still rename the App there).
GitHub redirects back to Weblate, which exchanges the temporary code for the App ID, private key, webhook secret, and slug and stores them in the database. The Connect GitHub account button is available immediately afterwards.
The manifest requests the permissions and event subscriptions Weblate needs
(Contents and Pull requests read/write, Metadata read-only,
Organization administration read-only, Workflows read/write, and the
Installation, Meta, Push and Repository events), and sets the
callback, setup and per-app webhook URLs automatically, so no manual GitHub App
configuration is required. GitHub delivers the Installation and
Installation repositories events to all GitHub Apps by default.
GitHub only offers accounts where the signed-in GitHub user can install or request the app. If an organization is not shown during the install flow, check the user’s organization role and the organization’s GitHub App installation restrictions. On GitHub.com, public apps can be installed on other accounts; private apps can only be installed on the account that owns the app.
Connecting a workspace
Connected GitHub accounts are bound to a Weblate workspace. A user with project administration rights for any project in a workspace can connect a GitHub account on that workspace. After connecting, every project in the workspace can import components from repositories the GitHub App installation has access to. For organization accounts, Weblate verifies that the install-time GitHub user can administer the organization installation.
Projects that are not in a workspace cannot connect a GitHub account through the GitHub App.
Removing a connected GitHub account also uninstalls the App from GitHub when no other Weblate workspace uses that installation. If another workspace still uses the installation, Weblate removes only the selected workspace connection. Components imported through that connection lose access to their repositories. Removing a workspace uninstalls its connected accounts the same way.
Weblate removes the connection even when GitHub no longer knows about the installation, and keeps it only when GitHub could not be reached, so that the removal can be retried.
Components imported through the GitHub App flow use the dedicated GitHub (via Weblate GitHub app) VCS backend. The component settings UI keeps the repository URL read-only to prevent the App-issued credentials from being redirected to an unrelated repository.
Migrating existing components
Weblate reports an informational diagnostic for Git and GitHub pull request components that can be migrated to a registered Weblate GitHub App. Follow the Migrate to GitHub App link from the diagnostic to review all eligible components in the workspace.
Connect or update the GitHub account for the workspace, grant the App access to the listed repositories, and select the components to migrate. Weblate changes the selected components to the GitHub (via Weblate GitHub app) VCS backend, replaces their repository addresses with canonical HTTPS clone URLs, and removes separate push URLs because the App authenticates pushes to the source repository.
App webhook URL
Each registered Weblate GitHub App has its own webhook URL containing an opaque token that uniquely identifies a single registered App:
https://weblate.example.com/hooks/integrations/<webhook_token>/
Components using the GitHub (via Weblate GitHub app) VCS backend
are matched only through this dedicated endpoint. All generic forge webhook
endpoints exclude them from matching and response diagnostics, including
/hooks/github/. Legacy GitHub App deliveries sent to the generic endpoint
can match only components using a non-App VCS backend.
When a repository is renamed or transferred on GitHub, the Repository
event makes Weblate refresh the repositories of the connected GitHub account
and point the affected components to the new repository URL. Apps registered
before Weblate 2026.10.1 are not subscribed to this event; enable
Repository under Subscribe to events in the App
settings on GitHub.
Refreshing repositories of a connected GitHub account retargets such
components too, for example when the event was missed. Use
refresh_github_repositories to do this for all connected GitHub
accounts at once.
If you are not using a GitHub App, add the Weblate webhook in the repository settings (Webhooks) to receive notifications on every push to a GitHub repository, as shown on the image below:
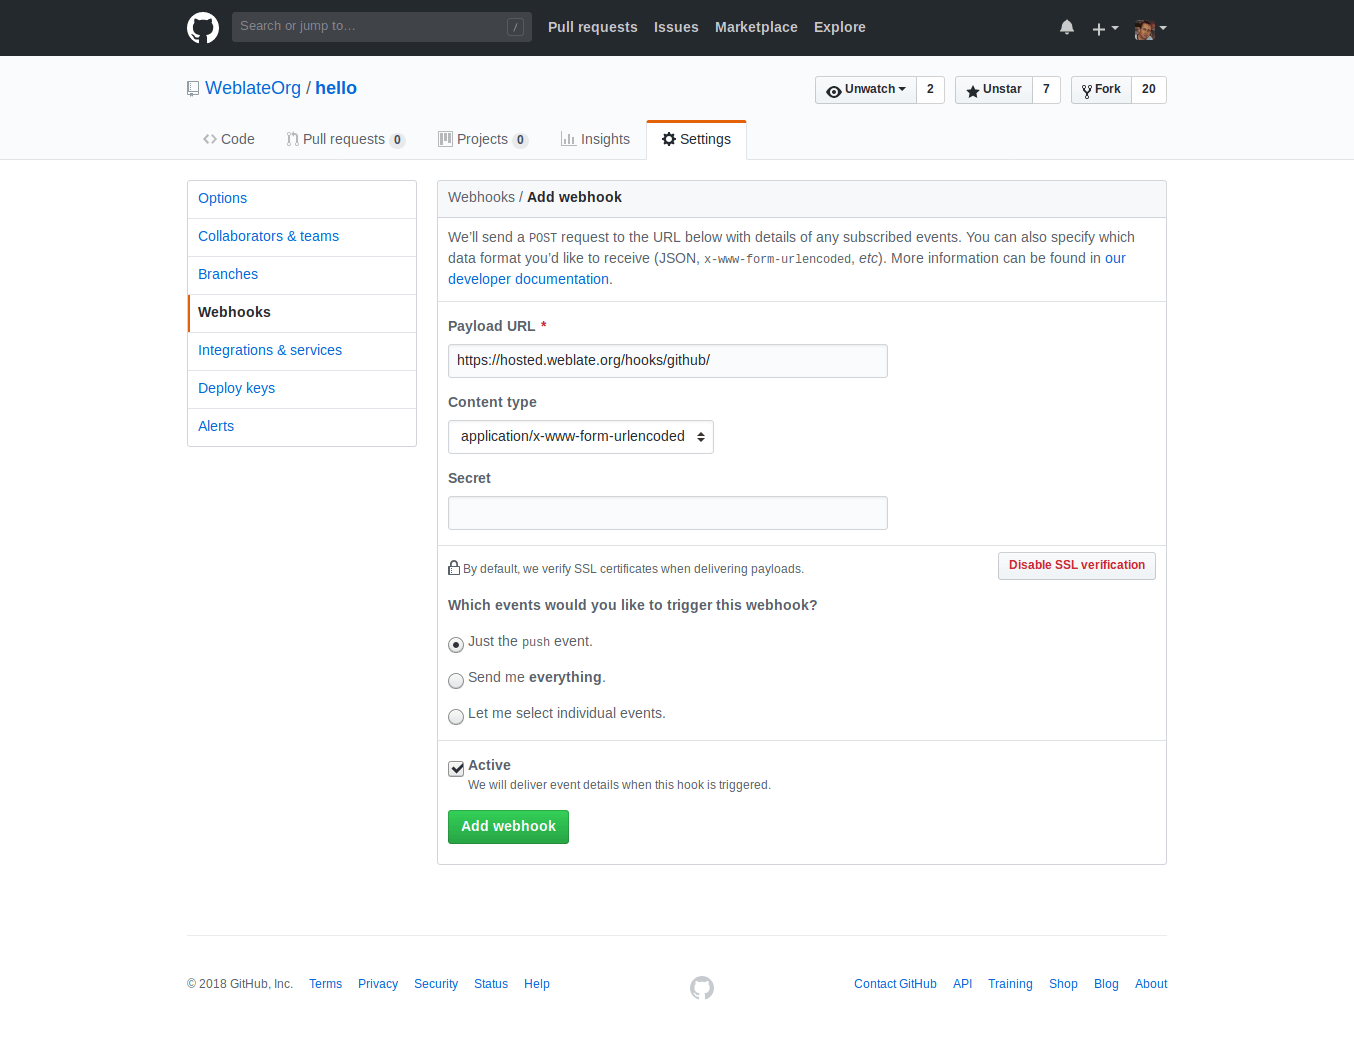
The Payload URL consists of your Weblate URL appended by
/hooks/github/, for example for the Hosted Weblate service, this is
https://hosted.weblate.org/hooks/github/.
You can leave other values at default settings. Weblate can handle both content types and consumes just the push event.
Requêtes de fusion GitHub
Ceci ajoute un simple niveau par dessus Git en utilisant GitHub API pour permettre de pousser les modifications de traduction en tant que demandes de tirage, au lieu de pousser directement sur le dépôt.
Git pushes changes directly to a repository, while the GitHub backend creates pull requests. The latter is not needed for merely accessing Git repositories.
To create pull requests, select GitHub as
Système de contrôle de version and configure GITHUB_CREDENTIALS. For
GitHub.com, use
api.github.com as the API host. The token must allow Weblate to read and
write repository contents and create pull requests. If Weblate should fork
private repositories, the token might also need administration access.
If creating a pull request fails with 404 Not Found, GitHub can be refusing
API access even when the repository is readable. Weblate checks the repository’s
pull request creation policy and, for user tokens, the authenticated account.
The failure alert reports confirmed findings and provides further checks when
the cause remains unknown. Diagnostic lookup failures preserve the original
pull request error.
Check that the effective API token belongs to the intended fork owner and allows creating pull requests. For fine-grained tokens, check repository selection, resource owner, and Pull requests write permission. Also check organization restrictions and access to the source branch. For GitHub Apps, check installation access to the repositories and pull request permissions. A successful Git push does not verify API access: pushing can use a separate SSH key. The repository log includes GitHub’s request ID and permission headers when available to help investigate the failure. Accepted permission headers describe endpoint requirements, not the permissions granted to the token.
GitLab
GitLab repository access
HTTPS with personal or project access token
For a single private repository, HTTPS access with an access token is usually the simplest setup when the provider supports Git over HTTPS. Use the provider-required username and token in Dépôt du code source.
Configure URL pour l’envoi du dépôt only when Weblate should push changes directly or when the chosen workflow requires a push URL, see Envoi des modifications depuis Weblate.
The token needs read access for cloning and write access for pushing. Provider-specific VCS backends that create pull or merge requests might require separate API credentials.
For GitLab, the token needs write_repository scope to be able to push changes to the repository. The project access token requires Developer role for pushing.
The URL needs to contain a username. For a personal access token, it is the
actual username:
https://user:personal_access_token@gitlab.com/example/example.git.
For project access tokens it can be a non-blank value:
https://example:project_access_token@gitlab.com/example/example.git.
Note
The rules for using project access tokens have changed between GitLab releases, the non-blank value is the current requirement, but older versions had different expectations (project name, bot user name). Check GitLab documentation matching your version if unsure.
SSH with a dedicated user
For setups with multiple repositories, use SSH access with a dedicated code
hosting user for Weblate. Add Weblate’s public SSH key to that user, grant the
user access to the repositories, and use SSH URLs in Dépôt du code source,
for example git@example.com:group/project.git.
Configure URL pour l’envoi du dépôt only when Weblate should push changes directly or when the chosen workflow requires a push URL, see Envoi des modifications depuis Weblate.
This also avoids provider restrictions on SSH key reuse. Some code hosting sites allow a public SSH key to be added only once, or only to a single user or deploy key entry. Keeping Weblate’s SSH key on a dedicated user lets that user be granted access to multiple repositories without reusing the key in several places.
This keeps personal, project, or API access tokens out of repository URLs. Provider API credentials are still needed when using a provider-specific VCS backend to create pull or merge requests; those credentials are configured separately from the Git repository URL.
For GitLab, create a dedicated user and use GitLab SSH URLs, for example
git@gitlab.com:group/project.git.
For Hosted Weblate repositories on GitLab, add the hosted weblate user with the required repository permissions, see Accès aux dépôts à partir de Hosted Weblate.
GitLab notifications
Weblate has support for GitLab hooks. Add a project webhook with destination
to /hooks/gitlab/ URL on your Weblate installation, for example
https://hosted.weblate.org/hooks/gitlab/.
Dépannage
Check GitLab webhook request history if webhooks are delivered.
The response payload contains information about matched components.
Requêtes de fusion GitLab
This adds a thin layer atop Git using the GitLab API to allow pushing translation changes as merge requests instead of pushing directly to the repository.
There is no need to use this to access Git repositories, ordinary Git works the same, the only difference is how pushing to a repository is handled. With Git changes are pushed directly to the repository, while the GitLab backend creates a merge request.
To create merge requests, select GitLab as
Système de contrôle de version and configure GITLAB_CREDENTIALS.
The Pousser la branche configuration affects where Weblate pushes changes before opening the merge request. If it is not set, the project is forked and changes are pushed through a fork. If it is set, changes are pushed to the upstream repository and chosen branch.
Gitea, Forgejo, and Codeberg
Gitea, Forgejo, and Codeberg repository access
HTTPS with an access token
For a single private repository, HTTPS access with an access token is usually the simplest setup when the provider supports Git over HTTPS. Use the provider-required username and token in Dépôt du code source.
Configure URL pour l’envoi du dépôt only when Weblate should push changes directly or when the chosen workflow requires a push URL, see Envoi des modifications depuis Weblate.
The token needs read access for cloning and write access for pushing. Provider-specific VCS backends that create pull or merge requests might require separate API credentials.
SSH with a dedicated user
For setups with multiple repositories, use SSH access with a dedicated code
hosting user for Weblate. Add Weblate’s public SSH key to that user, grant the
user access to the repositories, and use SSH URLs in Dépôt du code source,
for example git@example.com:group/project.git.
Configure URL pour l’envoi du dépôt only when Weblate should push changes directly or when the chosen workflow requires a push URL, see Envoi des modifications depuis Weblate.
This also avoids provider restrictions on SSH key reuse. Some code hosting sites allow a public SSH key to be added only once, or only to a single user or deploy key entry. Keeping Weblate’s SSH key on a dedicated user lets that user be granted access to multiple repositories without reusing the key in several places.
This keeps personal, project, or API access tokens out of repository URLs. Provider API credentials are still needed when using a provider-specific VCS backend to create pull or merge requests; those credentials are configured separately from the Git repository URL.
For Hosted Weblate repositories on Codeberg, add the hosted weblate user with the required repository permissions, see Accès aux dépôts à partir de Hosted Weblate.
Gitea notifications
Weblate has support for Gitea webhooks. Add a Gitea Webhook for
Push events event with destination to /hooks/gitea/ URL on your
Weblate installation, for example https://hosted.weblate.org/hooks/gitea/.
This can be done in Webhooks under repository Settings.
Forgejo notifications
Weblate has support for Forgejo webhooks. Add a Forgejo Webhook
for Push events event with destination to /hooks/forgejo/ URL
on your Weblate installation, for example
https://hosted.weblate.org/hooks/forgejo/. This can be done in
Webhooks under repository Settings.
Tirages Gitea demandés
Ajouté dans la version 4.12.
This adds a thin layer atop Git using the Gitea API to allow pushing translation changes as pull requests instead of pushing directly to the repository.
There is no need to use this to access Git repositories, ordinary Git works the same, the only difference is how pushing to a repository is handled. With Git changes are pushed directly to the repository, while the Gitea backend creates pull requests.
To create pull requests, select Gitea as
Système de contrôle de version and configure GITEA_CREDENTIALS.
Bitbucket
Bitbucket repository access
HTTPS with an access token
For a single private repository, HTTPS access with an access token is usually the simplest setup when the provider supports Git over HTTPS. Use the provider-required username and token in Dépôt du code source.
Configure URL pour l’envoi du dépôt only when Weblate should push changes directly or when the chosen workflow requires a push URL, see Envoi des modifications depuis Weblate.
The token needs read access for cloning and write access for pushing. Provider-specific VCS backends that create pull or merge requests might require separate API credentials.
SSH with a dedicated user
For setups with multiple repositories, use SSH access with a dedicated code
hosting user for Weblate. Add Weblate’s public SSH key to that user, grant the
user access to the repositories, and use SSH URLs in Dépôt du code source,
for example git@example.com:group/project.git.
Configure URL pour l’envoi du dépôt only when Weblate should push changes directly or when the chosen workflow requires a push URL, see Envoi des modifications depuis Weblate.
This also avoids provider restrictions on SSH key reuse. Some code hosting sites allow a public SSH key to be added only once, or only to a single user or deploy key entry. Keeping Weblate’s SSH key on a dedicated user lets that user be granted access to multiple repositories without reusing the key in several places.
This keeps personal, project, or API access tokens out of repository URLs. Provider API credentials are still needed when using a provider-specific VCS backend to create pull or merge requests; those credentials are configured separately from the Git repository URL.
For Hosted Weblate repositories on Bitbucket, add the hosted weblate user with the required repository permissions, see Accès aux dépôts à partir de Hosted Weblate.
To push directly, use Git or Mercurial with URL pour l’envoi du dépôt.
Bitbucket notifications
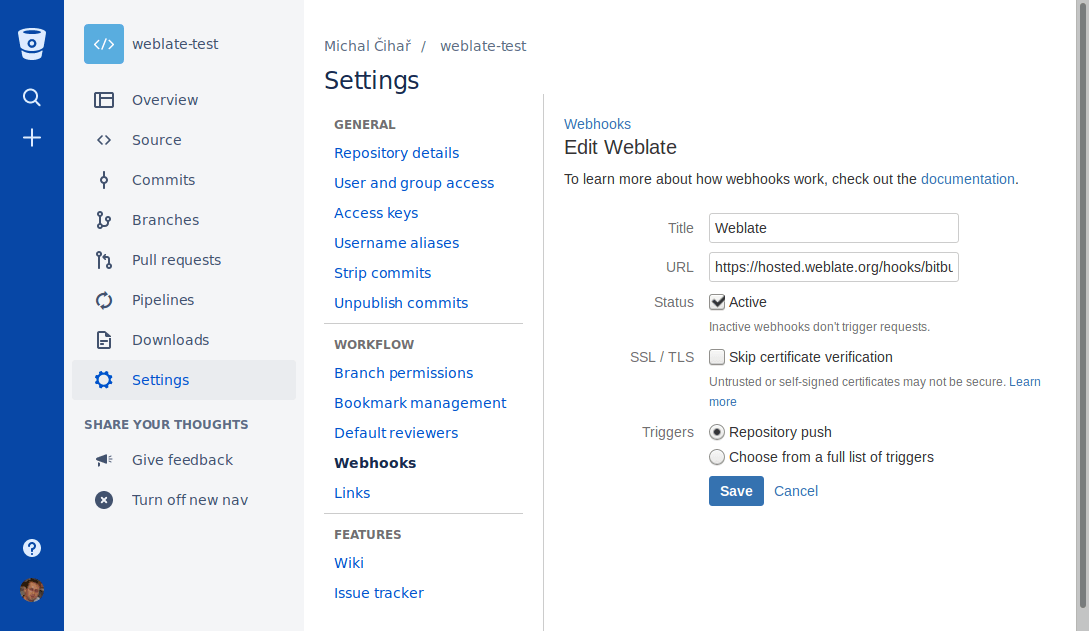
Weblate has support for Bitbucket webhooks. Add a webhook which triggers upon
repository push, with destination to /hooks/bitbucket/ URL on your Weblate
installation, for example https://hosted.weblate.org/hooks/bitbucket/.
Tirages demandés du Bitbucket Data Center
Ajouté dans la version 4.16.
This adds a thin layer atop Git using the Bitbucket Data Center API to allow pushing translation changes as pull requests instead of pushing directly to the repository.
Avertissement
Ceci ne prend pas en charge l’API Bitbucket Cloud.
There is no need to use this to access Git repositories, ordinary Git works the same, the only difference is how pushing to a repository is handled. With Git changes are pushed directly to the repository, while the Bitbucket Data Center backend creates a pull request.
To create pull requests, select Bitbucket Data Center as
Système de contrôle de version and configure BITBUCKETSERVER_CREDENTIALS.
Requêtes de pull de Bitbucket Cloud
Ajouté dans la version 5.8.
This adds a thin layer atop Git using the Bitbucket Cloud API to allow pushing translation changes as pull requests instead of pushing directly to the repository.
Avertissement
Ceci est différent de l’API Bitbucket Data Center.
There is no need to use this to access Git repositories, ordinary Git works the same, the only difference is how pushing to a repository is handled. With Git changes are pushed directly to the repository, while the Bitbucket Cloud backend creates a pull request.
To create pull requests, select Bitbucket Cloud as
Système de contrôle de version and configure BITBUCKETCLOUD_CREDENTIALS.
Azure DevOps
Azure Repos repository access
HTTPS with an access token
For a single private repository, HTTPS access with an access token is usually the simplest setup when the provider supports Git over HTTPS. Use the provider-required username and token in Dépôt du code source.
Configure URL pour l’envoi du dépôt only when Weblate should push changes directly or when the chosen workflow requires a push URL, see Envoi des modifications depuis Weblate.
The token needs read access for cloning and write access for pushing. Provider-specific VCS backends that create pull or merge requests might require separate API credentials.
Use the HTTPS clone URL shown by Azure Repos for the repository.
SSH with a dedicated user
For setups with multiple repositories, use SSH access with a dedicated code
hosting user for Weblate. Add Weblate’s public SSH key to that user, grant the
user access to the repositories, and use SSH URLs in Dépôt du code source,
for example git@example.com:group/project.git.
Configure URL pour l’envoi du dépôt only when Weblate should push changes directly or when the chosen workflow requires a push URL, see Envoi des modifications depuis Weblate.
This also avoids provider restrictions on SSH key reuse. Some code hosting sites allow a public SSH key to be added only once, or only to a single user or deploy key entry. Keeping Weblate’s SSH key on a dedicated user lets that user be granted access to multiple repositories without reusing the key in several places.
This keeps personal, project, or API access tokens out of repository URLs. Provider API credentials are still needed when using a provider-specific VCS backend to create pull or merge requests; those credentials are configured separately from the Git repository URL.
Use the SSH URL shown by Azure Repos for the repository.
Azure Repos notifications
Weblate has support for Azure Repos webhooks. Add a webhook for
Code pushed event with destination to /hooks/azure/ URL on your
Weblate installation, for example https://hosted.weblate.org/hooks/azure/.
This can be done in Service hooks under Project
settings.
Poussées Azure DevOps demandées
Ceci ajoute un niveau supplémentaire par dessus Git en utilisant Azure DevOps API pour permettre de pousser les modifications des traductions comme des requêtes pour pousser sur le dépôt, au lieu de les pousser directement.
Git pushes changes directly to a repository, while the Azure DevOps backend creates pull requests. The latter is not needed for merely accessing Git repositories.
To create pull requests, select Azure DevOps as
Système de contrôle de version and configure AZURE_DEVOPS_CREDENTIALS.
Pagure
Pagure repository access
HTTPS with an access token
For a single private repository, HTTPS access with an access token is usually the simplest setup when the provider supports Git over HTTPS. Use the provider-required username and token in Dépôt du code source.
Configure URL pour l’envoi du dépôt only when Weblate should push changes directly or when the chosen workflow requires a push URL, see Envoi des modifications depuis Weblate.
The token needs read access for cloning and write access for pushing. Provider-specific VCS backends that create pull or merge requests might require separate API credentials.
SSH with a dedicated user
For setups with multiple repositories, use SSH access with a dedicated code
hosting user for Weblate. Add Weblate’s public SSH key to that user, grant the
user access to the repositories, and use SSH URLs in Dépôt du code source,
for example git@example.com:group/project.git.
Configure URL pour l’envoi du dépôt only when Weblate should push changes directly or when the chosen workflow requires a push URL, see Envoi des modifications depuis Weblate.
This also avoids provider restrictions on SSH key reuse. Some code hosting sites allow a public SSH key to be added only once, or only to a single user or deploy key entry. Keeping Weblate’s SSH key on a dedicated user lets that user be granted access to multiple repositories without reusing the key in several places.
This keeps personal, project, or API access tokens out of repository URLs. Provider API credentials are still needed when using a provider-specific VCS backend to create pull or merge requests; those credentials are configured separately from the Git repository URL.
Pagure notifications
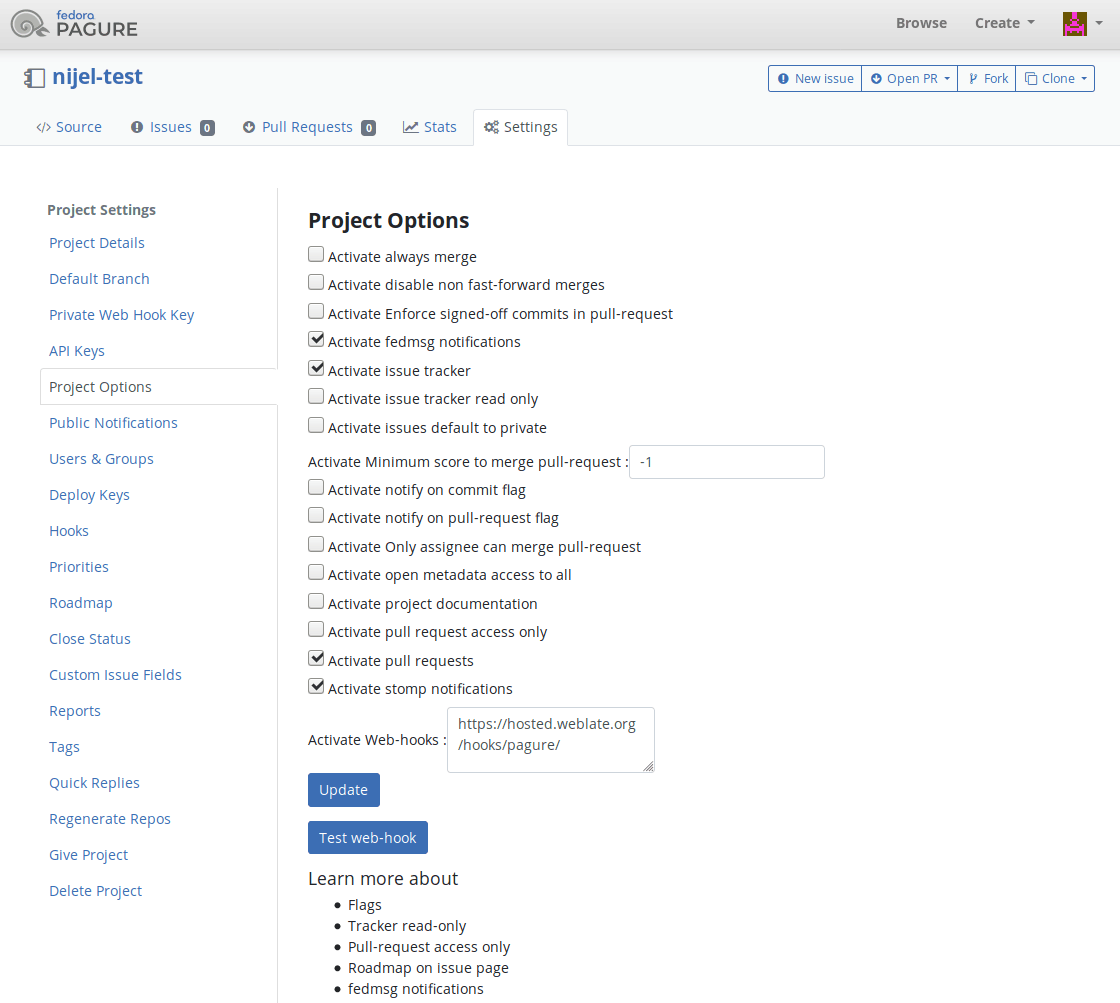
Weblate has support for Pagure hooks. Add a webhook with destination to
/hooks/pagure/ URL on your Weblate installation, for example
https://hosted.weblate.org/hooks/pagure/. This can be done in
Activate Web-hooks under Project options:
Requêtes de fusion Pagure
Ajouté dans la version 4.3.2.
This adds a thin layer atop Git using the Pagure API to allow pushing translation changes as merge requests instead of pushing directly to the repository.
There is no need to use this to access Git repositories, ordinary Git works the same, the only difference is how pushing to a repository is handled. With Git changes are pushed directly to the repository, while the Pagure backend creates a merge request.
To create merge requests, select Pagure as
Système de contrôle de version and configure PAGURE_CREDENTIALS.
Other workflows
Gitee repository access
HTTPS with an access token
For a single private repository, HTTPS access with an access token is usually the simplest setup when the provider supports Git over HTTPS. Use the provider-required username and token in Dépôt du code source.
Configure URL pour l’envoi du dépôt only when Weblate should push changes directly or when the chosen workflow requires a push URL, see Envoi des modifications depuis Weblate.
The token needs read access for cloning and write access for pushing. Provider-specific VCS backends that create pull or merge requests might require separate API credentials.
SSH with a dedicated user
For setups with multiple repositories, use SSH access with a dedicated code
hosting user for Weblate. Add Weblate’s public SSH key to that user, grant the
user access to the repositories, and use SSH URLs in Dépôt du code source,
for example git@example.com:group/project.git.
Configure URL pour l’envoi du dépôt only when Weblate should push changes directly or when the chosen workflow requires a push URL, see Envoi des modifications depuis Weblate.
This also avoids provider restrictions on SSH key reuse. Some code hosting sites allow a public SSH key to be added only once, or only to a single user or deploy key entry. Keeping Weblate’s SSH key on a dedicated user lets that user be granted access to multiple repositories without reusing the key in several places.
This keeps personal, project, or API access tokens out of repository URLs. Provider API credentials are still needed when using a provider-specific VCS backend to create pull or merge requests; those credentials are configured separately from the Git repository URL.
Gitee notifications
Weblate has support for Gitee webhooks. Add a WebHook for
Push event with destination to /hooks/gitee/ URL on your
Weblate installation, for example https://hosted.weblate.org/hooks/gitee/.
This can be done in WebHooks under repository
Management.
Gerrit review requests
Gerrit support adds a thin layer atop Git using the git-review tool to allow pushing translation changes as Gerrit review requests, instead of pushing them directly to the repository.
The optional Pousser la branche setting selects the target branch for
the Gerrit review. Leave it empty to use Branche du dépôt. Use the short
branch name, such as main; Weblate and git-review push the review to
refs/for/<branch> automatically. Gerrit push options can be appended after
% in either setting, for example main%topic=l10n. Gerrit interprets
these options as the configured Weblate Gerrit account and applies its own
permissions.
The Gerrit documentation has the details on the configuration necessary to set up such repositories. There is no separate code-hosting credential setting for this backend.
Docker credentials
For Docker installations, code-hosting API credentials can also be provided through environment variables, see Code-hosting sites credentials.